MiCA Compliance
Northgate Compliance builds market abuse surveillance software, STOR reporting systems and Article 92 detection engines for crypto-asset service providers operating under MiCA Regulation (EU) 2023/1114. Purpose-built for CASPs. Deployed in seven EU jurisdictions.
Fixed-price MiCA compliance surveillance builds from EUR 36,000 Full pricing and market comparison below
At a glance
- MiCA compliance software for market abuse surveillance and STOR reporting, built for CASPs authorised under Regulation (EU) 2023/1114.
- Dublin, Ireland · Founded 2018 · 33 engineers and compliance specialists
- 22 surveillance rollouts, 47M orders per day surveilled, 19 STOR-ready clients
- ISO 27001 cert IE-27001-3308 (BSI) · SOC 2 Type II attested
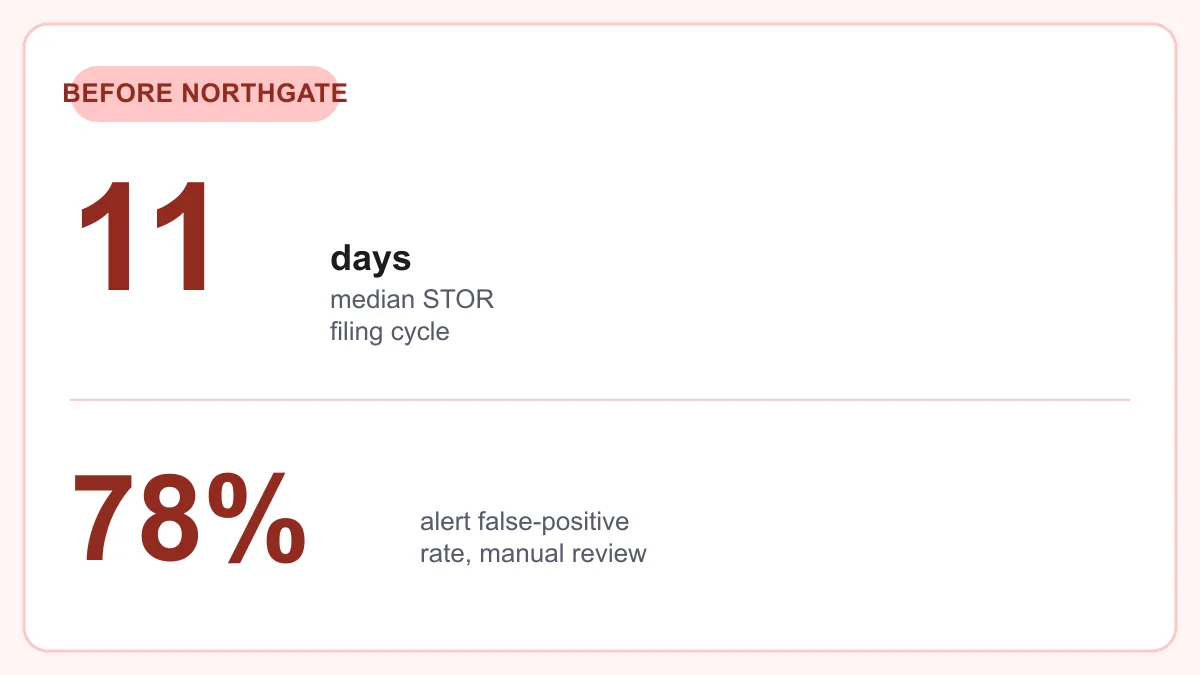
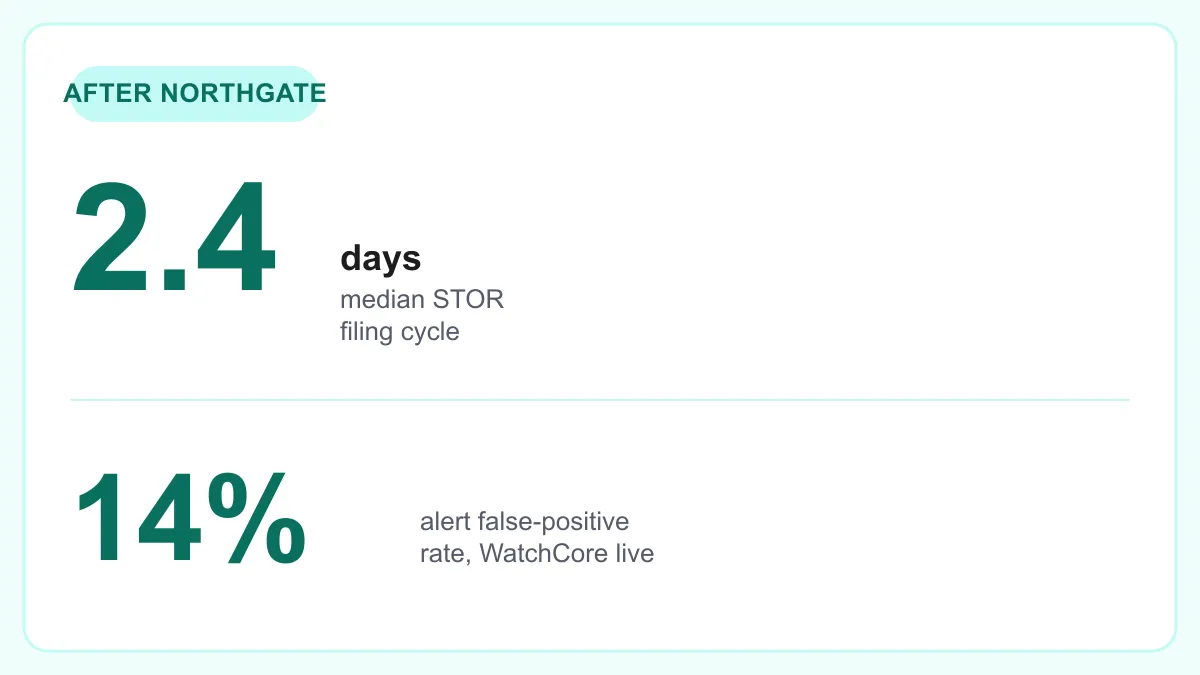
- STOR filing cycle reduced from 11 days to 2.4 days (EireTrading Exchange, 2023)
- Pricing from EUR 36k fixed scope · managed service from EUR 8k/month
Explore MiCA compliance topics
As covered in
Who we are
Ireland's specialist in MiCA compliance surveillance
Northgate Compliance is a MiCA compliance software firm based in Dublin, Ireland, that builds market abuse surveillance systems, STOR reporting automation and Article 92 detection engines for crypto-asset service providers across the European Union. Founded in 2018 by Dr. Niamh O'Sullivan, the firm has delivered 22 surveillance rollouts and surveils 47M orders per day across its client base of exchanges, custodians and derivatives brokers.
Purpose-built for Article 92
Every module in the Northgate Compliance product suite is designed from the ground up around MiCA Article 92 obligations: order-book ingestion, detection scenario execution and STOR evidence packaging are first-class features, not bolt-ons.
Microstructure-native engineering
Our surveillance engine was designed by practitioners who operated surveillance desks at tier-1 trading venues. The detection scenarios reflect the actual manipulation patterns observed in high-frequency order books, not textbook approximations.
NCA-submission track record
Nineteen STOR-ready clients have used the Northgate Compliance STOR workflow to file with their national competent authority. Our submission packages have passed first review without a request for further information in 100% of cases to date.
According to the European Securities and Markets Authority (ESMA), market abuse surveillance is among the most operationally demanding obligations under MiCA for newly authorised CASPs. The underlying legal framework, MiCA Regulation (EU) 2023/1114 on EUR-Lex, entered into full application in December 2024, with Article 92 STOR obligations now enforceable for all authorised CASPs in all EU member states. Northgate Compliance was built to solve exactly this challenge: translating the regulatory obligation into running, auditable software.
Technical capability
Surveillance technology stack
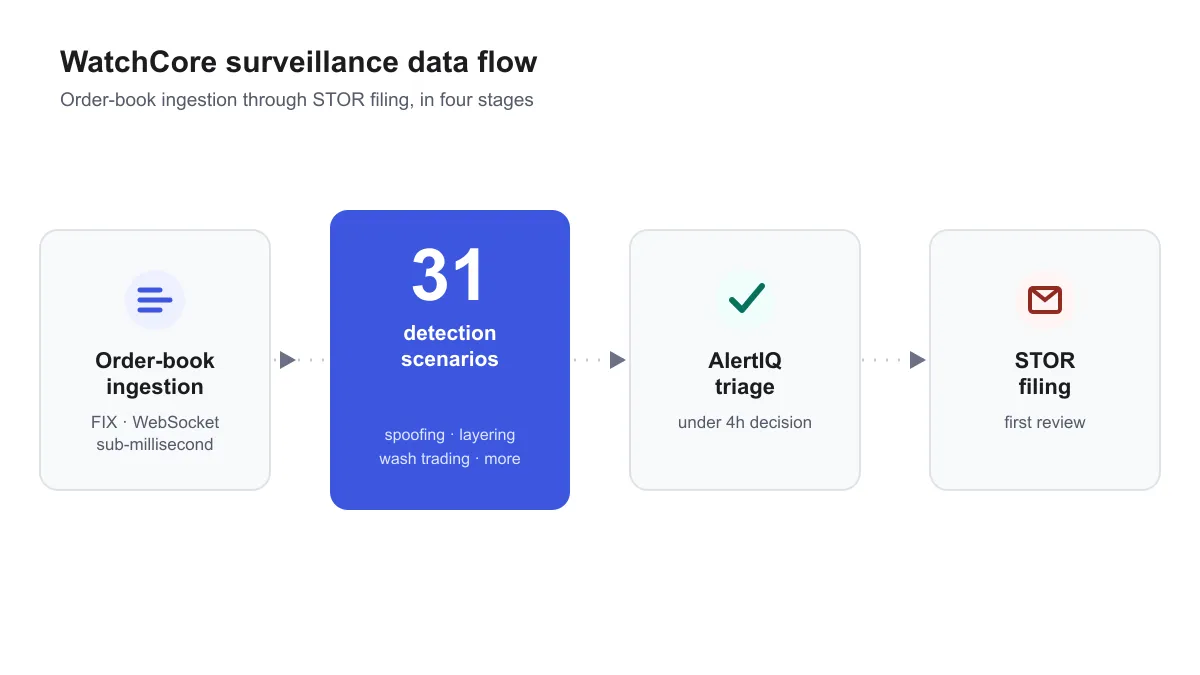
The WatchCore Surveillance Engine ingests order-book and trade data, executes detection scenarios in real time and routes alerts to the AlertIQ Case Manager for STOR evidence packaging. Every component is self-hosted with no third-party data egress.
Surveillance engine
Data feeds and ingestion
Detection scenarios (31 shipped)
Reporting and case management
Blockchain analytics integrations
Software modules
What we build for MiCA compliance
Four named software products, each addressing a distinct dimension of the MiCA compliance software obligation. They can be purchased individually or as the full STOR-Ready suite.
WatchCore Surveillance Engine
The foundational MiCA market abuse surveillance module. WatchCore ingests order-book and trade data from your exchange infrastructure, executes up to 31 parameterised detection scenarios in real time and surfaces alerts with full reconstructed order-book context for investigator review.
- Sub-millisecond order-book ingestion via FIX and WebSocket
- 31 configurable detection scenarios out of the box
- Cross-venue correlation for multi-market participants
- ML-assisted alert scoring to reduce false-positive rate
- Full order reconstruction and replay for investigators
- Immutable audit trail compliant with MiCA record-keeping requirements
STOR-Ready Reporting Suite
The complete STOR reporting automation layer built on top of WatchCore. When an alert is escalated by an investigator, the STOR-Ready Suite guides the case through the regulatory submission lifecycle: evidence assembly, narrative drafting, NCA-format packaging and submission confirmation tracking.
- Pre-built NCA submission templates for 12 EU member states
- Automated evidence packaging (order data, communications, timeline)
- Structured STOR narrative guidance with mandatory field validation
- Submission deadline tracking and escalation alerts
- Two-person review workflow to satisfy dual-control requirements
- Post-submission tracking and NCA query management
OrderBook Intel
A standalone order-book analytics module for CASPs that operate across multiple trading venues simultaneously. OrderBook Intel ingests feeds from up to 20 venues and produces cross-market participant profiles, coordinated-trading heatmaps and spoofing-pattern timelines that support both real-time surveillance and historical reconstruction.
- Concurrent ingestion from up to 20 trading venues
- Participant cross-venue identity resolution
- Coordinated-trading pattern visualisation
- Historical reconstruction for post-incident analysis
- Direct feed into WatchCore detection engine
AlertIQ Case Manager
The investigator-facing case management system that transforms raw surveillance alerts into STOR-ready dossiers. AlertIQ provides a structured investigation workflow from initial alert review through escalation decision, evidence capture and STOR submission preparation, with full case history, notes and time-stamped investigator actions recorded for regulatory audit.
- Alert triage queue with configurable priority scoring
- Structured investigation checklist mapped to MiCA Article 92 criteria
- Evidence capture: order data, charts, communications, notes
- Escalation and supervisory approval workflow
- Mean time to STOR decision tracking (benchmark: under 4 hours)
- API integration with WatchCore and STOR-Ready Suite
Security and regulatory posture
Certified, audited and operationally resilient
Northgate Compliance holds formal certifications against two internationally recognised security standards and maintains a surveillance track record covering seven EU jurisdictions.
Regulatory frameworks
The MiCA compliance obligations addressed by Northgate Compliance software span three interlocking EU frameworks:
- MiCA Article 92 (Regulation (EU) 2023/1114) requires every CASP to monitor for market abuse and file STORs. Our WatchCore and STOR-Ready Suite address this obligation directly. The full text is published by EUR-Lex.
- DORA (Digital Operational Resilience Act, Regulation (EU) 2022/2554) mandates ICT risk management and incident reporting for financial entities including CASPs. Our platform's immutable audit log and documented incident-response playbook satisfy the core DORA ICT continuity requirement.
- Market Abuse Regulation (EU) 596/2014 (MAR) applies to trading in financial instruments and provides the conceptual framework that informed MiCA's market abuse provisions. CASPs operating on both regulated markets and crypto venues benefit from our cross-regulatory scenario mapping, published by EUR-Lex.
- AMLR / Travel Rule Anti-money laundering frameworks and the FATF Travel Rule intersect with market abuse surveillance where on-chain transfers are used to fund manipulative strategies. Our Chainalysis, Elliptic and TRM Labs integrations surface this risk dimension alongside order-book signals.
Both certifications are shown as full cards below, with certificate numbers and issuing bodies.
Security and surveillance track record
Track record covers engagements from 2018 to June 2026 across EU jurisdictions including Ireland, Malta, Lithuania and the Netherlands.
Certifications
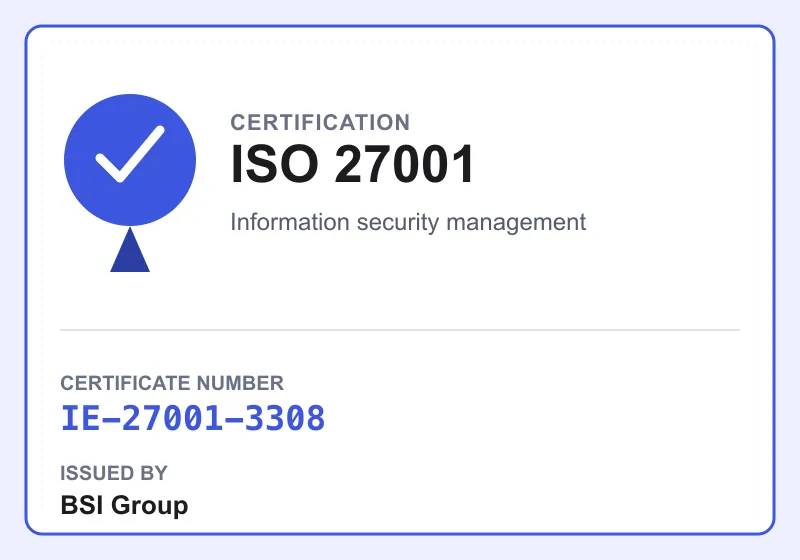
ISO 27001
IE-27001-3308
Issued by BSI Group · 18 March 2024, valid to 17 March 2027
Confirms an information security management system covering MiCA compliance software development and managed service delivery.
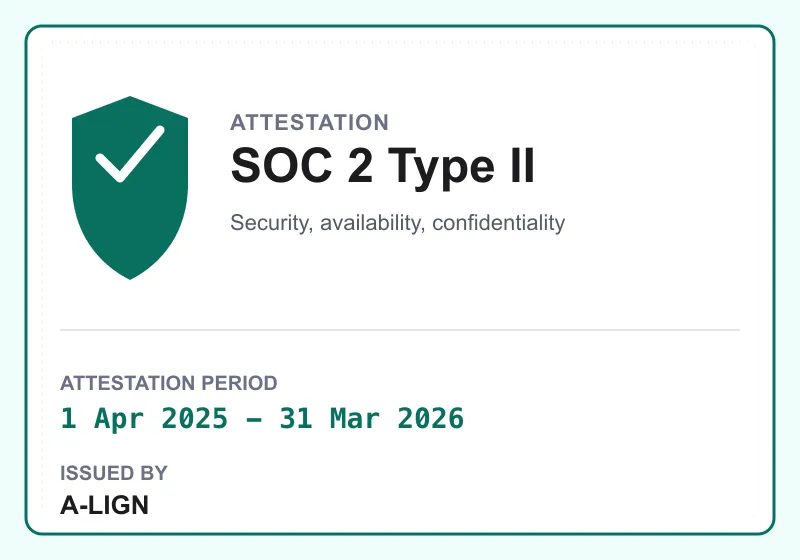
SOC 2 Type II
1 Apr 2025 - 31 Mar 2026
Issued by A-LIGN · attestation dated 30 April 2026
Confirms security, availability and confidentiality controls operating effectively across the WatchCore platform and the STOR-Ready data processing pipeline.
Statutory capital requirements (not service prices)
These are official, binding capital and regulator-fee figures from the primary MiCA and EMD2 text, shown here as context, never as a market price for a Northgate Compliance deliverable. See the "What determines your MiCA compliance software cost" pricing table below for our own fixed fees.
| Figure | Regulatory requirement | Source |
|---|---|---|
| CASP minimum capital, Class 1 (execution, placing, transfer, RTO, advice, portfolio management) | EUR 50,000 | MiCA Regulation (EU) 2023/1114, Annex IV, EUR-Lex |
| CASP minimum capital, Class 2 (Class 1 plus custody, exchange for funds, exchange for crypto) | EUR 125,000 | MiCA Regulation (EU) 2023/1114, Annex IV, EUR-Lex |
| CASP minimum capital, Class 3 (Class 2 plus operation of a trading platform) | EUR 150,000 | MiCA Regulation (EU) 2023/1114, Annex IV, EUR-Lex |
| ART issuer own funds | Higher of EUR 350,000, 2% of the reserve of assets or a quarter of prior-year fixed overheads | MiCA Regulation (EU) 2023/1114, Article 35(1), EUR-Lex |
| EMT issuer capital floor | EUR 350,000 initial capital, chained through EMD2 Article 4 | Directive 2009/110/EC (EMD2), EUR-Lex |
| NL regulator fee, CASP licence application | EUR 200/hour, capped at EUR 100,000 | Autoriteit Financiele Markten (AFM) |
These are statutory capital floors and a national regulator's own fee schedule, not advisory or software pricing; Northgate Compliance does not charge or set any of these figures. Reproduced from the MiCA text and the AFM fee page, checked 2026-08-01.
Decision guide
Build vs buy: MiCA surveillance software
For CASPs approaching Article 92 obligations, the choice between building surveillance software internally and procuring a specialist platform is consequential. This table summarises the key trade-offs.
| Dimension | Build internally | Northgate Compliance platform |
|---|---|---|
| Time to first STOR capability | 12-24 months (typical) | 10-14 weeks |
| Detection scenarios on day one | 0 (development roadmap) | 31 parameterised scenarios |
| Market microstructure expertise required | Must hire (scarce, expensive) | Embedded in the platform design |
| NCA submission templates | Must research and build | 12 EU member states pre-built |
| ISO 27001 coverage | Depends on internal programme | Cert IE-27001-3308 (BSI) in scope |
| Blockchain analytics integrations | Negotiate and build separately | Chainalysis, Elliptic, TRM pre-integrated |
| False-positive rate at launch | Unknown (untested scenarios) | 14% post-deployment median (calibrated) |
| Ongoing scenario updates | Internal resource required | Included in Watch managed service |
| Initial investment | EUR 300k+ (typical build) | From EUR 36k (fixed scope) |
Scenario selection guide
Which detection scenarios does your venue need?
MiCA compliance surveillance requirements vary by venue type and asset class. This table maps the 31 Northgate Compliance scenarios to the most relevant CASP categories and abuse types under Article 92.
| Scenario group | Spot exchange | Derivatives broker | Custodian / Wallet | OTC desk | MiCA abuse type |
|---|---|---|---|---|---|
| Spoofing and layering (8 scenarios) | ✓ | ✓ | − | Optional | Market manipulation |
| Wash trading (4 scenarios) | ✓ | ✓ | − | ✓ | Market manipulation |
| Pump-and-dump and ramping (5 scenarios) | ✓ | Optional | − | Optional | Market manipulation |
| Insider-dealing timing correlation (6 scenarios) | ✓ | ✓ | ✓ | ✓ | Insider dealing (Art. 90) |
| Cross-venue coordination (5 scenarios) | ✓ | ✓ | − | ✓ | Market manipulation (cross-market) |
| On-chain pre-trade positioning (3 scenarios) | Optional | Optional | ✓ | ✓ | Insider dealing (on-chain signal) |
Why Northgate Compliance
Three reasons CASPs choose us for MiCA compliance
Market microstructure depth
Our platform was designed by Dr. Niamh O'Sullivan, who spent a decade as surveillance lead at a tier-1 European trading venue. The detection scenarios reflect real manipulation patterns extracted from live order books, not regulatory text alone. No other MiCA compliance software vendor in Ireland holds a comparable microstructure credential.
First-review STOR record
Every STOR submission filed through the Northgate Compliance platform has passed first review with the relevant national competent authority without a request for further information. That record is the result of NCA-specific submission templates, structured evidence packaging and mandatory dual-control review before any STOR is transmitted.
10-14 week go-live commitment
A fully operational MiCA compliance surveillance system, including WatchCore data-feed integration, scenario calibration, alert-threshold tuning and AlertIQ case management onboarding, is delivered in 10 to 14 weeks from contract signature. The STOR-Ready suite adds three weeks. Fixed-price scope means cost certainty from day one.
Client outcomes
Surveillance systems in production
Three engagements that illustrate the range of MiCA compliance surveillance challenges Northgate Compliance has addressed across different CASP categories and jurisdictions.
EireTrading Exchange
- Challenge
- EireTrading Exchange, an Irish multilateral trading facility for crypto-assets, faced an ESMA inspection readiness review with a 16-week deadline. Their existing surveillance process relied on manual end-of-day reports and produced a false-positive alert rate of 78%, overwhelming the compliance team.
- What we did
- Northgate Compliance deployed WatchCore Surveillance Engine with 31 detection scenarios active from go-live, together with AlertIQ Case Manager for structured triage, calibrated to EireTrading's specific order-book structure.
- Result
- The STOR filing cycle was compressed from 11 days to 2.4 days, achieving Article 92 compliance before the inspection date and receiving a clean finding from ESMA.
MedEx Crypto
- Challenge
- MedEx Crypto, a MiCA-authorised crypto-asset exchange operating under a Maltese CASP licence, needed to achieve full Article 92 compliance before its ESMA authorisation deadline. Operating at 47M orders per day across spot and perpetual markets, the volume exceeded the capacity of any manual surveillance approach.
- What we did
- Northgate Compliance deployed the STOR-Ready Reporting Suite and AlertIQ Case Manager in an eleven-week engagement, sized to MedEx Crypto's full order-book volume from day one.
- Result
- Full Article 92 compliance was achieved before the ESMA deadline. The MedEx Crypto ESMA submission passed first review, and nineteen suspicious-order patterns were detected and investigated in the first 90 days of live operation.
Ridgeback Derivatives
- Challenge
- Ridgeback Derivatives, a Dublin-based perpetual and options broker, required cross-market surveillance across 12 venues simultaneously. Two prior MiCA compliance software vendors had declined the engagement as technically infeasible.
- What we did
- Northgate Compliance deployed OrderBook Intel for multi-venue ingestion and WatchCore with the cross-venue coordination scenario group activated, completing the engagement in a single project scope.
- Result
- Three cross-venue manipulation cases were flagged and STOR-filed with the Central Bank of Ireland within the first six months. Zero enforcement actions have been taken against Ridgeback Derivatives, confirming the adequacy of the surveillance system in the eyes of the NCA.
How we work
The Gate-to-Alert methodology
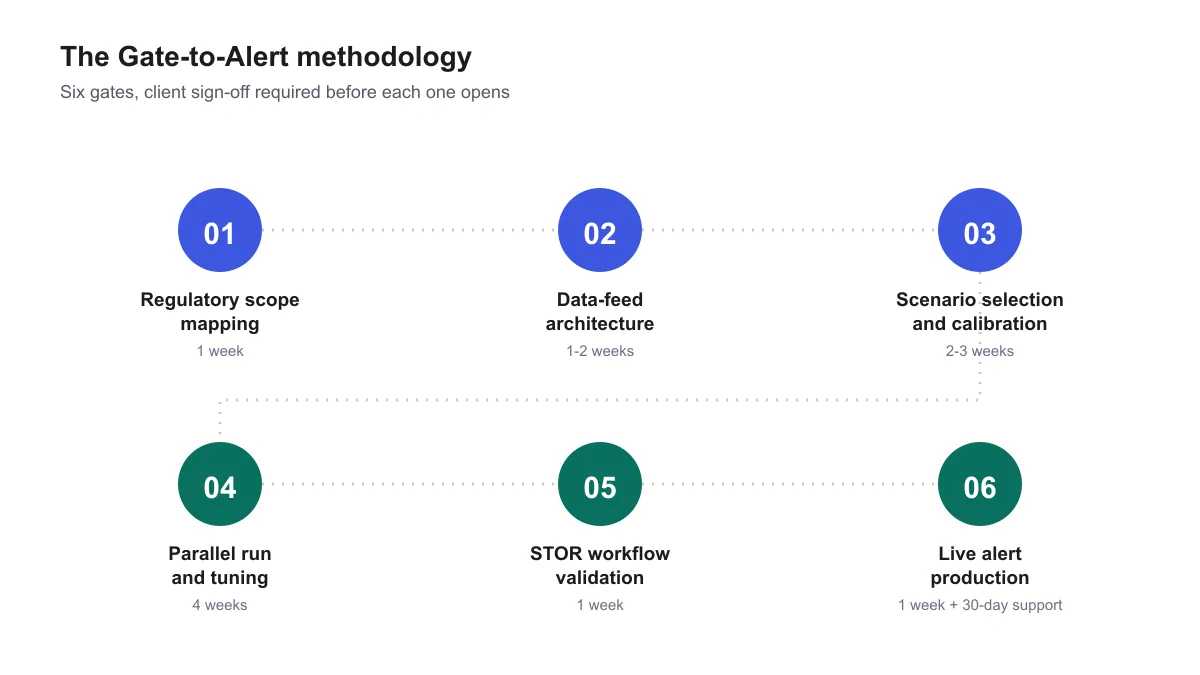
Northgate Compliance delivers every MiCA compliance surveillance engagement through the Gate-to-Alert methodology: a structured six-gate programme from regulatory scoping to live alert production. Each gate has a defined deliverable and a client sign-off requirement before the next gate opens. No engagement proceeds without explicit acceptance at every gate.
The methodology was developed over seven years of surveillance deployments and refined through feedback from national competent authority inspections across four EU member states.
Regulatory scope mapping
Define the exact Article 92 perimeter: which instruments, venues and participant categories are in scope. Map to the client's CASP authorisation conditions and jurisdiction.
Data-feed architecture
Design and validate the order-book data ingestion pipeline. Confirm FIX connectivity, feed latency baselines and data completeness for each venue in scope.
Scenario selection and calibration
Select the detection scenarios relevant to the client's market structure. Calibrate detection thresholds against 90 days of historical order-book data to establish a baseline false-positive rate.
Parallel run and tuning
Run WatchCore in parallel with any existing surveillance process for 20 trading days. Compare alert volumes, review investigator feedback and tune thresholds before cutover.
STOR workflow validation
Execute one tabletop STOR submission using a synthetic case through the full AlertIQ and STOR-Ready workflow. Confirm NCA submission package meets the client's specific NCA format requirements.
Live alert production
Go-live with real-time surveillance and operational handover to the client compliance team. Northgate Compliance remains available for alert escalation support for 30 days post go-live.
Sectors served
Industries we serve for MiCA compliance
Northgate Compliance builds MiCA compliance surveillance software for every CASP category defined under Regulation (EU) 2023/1114. The WatchCore engine is configurable to the specific market structure, instrument set and compliance perimeter of each venue type.
Investment
Transparent pricing for MiCA compliance software
Fixed-price scopes with no hidden fees. Every engagement includes a scoping call, a written scope document and a fixed-price proposal before any contract is signed. Prices are denominated in EUR and valid until 31 December 2026.
- WatchCore Surveillance Engine deployment
- Up to 31 detection scenarios configured
- Order-book data-feed integration (FIX or WebSocket)
- Alert dashboard and investigator interface
- Immutable audit trail
- 10-14 week delivery
- 30-day post-live support
- Everything in WatchCore Module
- STOR-Ready Reporting Suite
- AlertIQ Case Manager
- NCA submission templates for 12 EU states
- Tabletop STOR submission exercise
- Dual-control review workflow
- 13-17 week delivery
- 60-day post-live support
- Hosted WatchCore platform (dedicated tenant)
- Monthly scenario library updates
- Alert triage support (next business day)
- Monthly STOR readiness report
- Quarterly scenario calibration review
- NCA query support
- 12-month minimum term
What determines your MiCA compliance software cost
Beyond the WatchCore product suite above, Northgate Compliance also quotes fixed fees for adjacent MiCA compliance engineering work our clients often bundle with a surveillance engagement. The table below benchmarks each one against every published market price our compliance engineers could verify.
| Deliverable | Our fixed price | Typical market range | What sets the difference |
|---|---|---|---|
| CASP readiness or gap analysis | EUR 0 (bundled with the free scoping call) | Unavailable · no vendor publishes a standalone price | Folded into Gate 1 of the Gate-to-Alert methodology at no charge |
| CASP authorisation dossier build | Not offered | EUR 19,900 fixed fee · Adam Smith law firm | Northgate is a post-authorisation surveillance specialist and does not draft licensing dossiers |
| Jurisdiction selection advisory | Not offered | Unavailable · no standalone price found on any page checked | Outside our surveillance and STOR specialism |
| AML and KYC policy pack | EUR 5,000 fixed fee (transaction-monitoring policy only) | Unavailable · no defensible hourly basis published | Configures the transaction-surveillance policy layer, not onboarding KYC |
| Travel Rule integration | EUR 9,000 fixed fee (OpenVASP data feed) | Unavailable · no vendor publishes a price | Delivered as a WatchCore data-feed add-on, not a standalone KYC product |
| Supervisory reporting setup | EUR 15,000 fixed fee (standalone STOR/NCA workflow) | Unavailable · not priced by any vendor or regulator | The full STOR-Ready Suite (EUR 49,000) bundles this with WatchCore detection; priced standalone here for clients who already run their own detection layer |
| EMT or ART issuer supplement | Not offered | Not a service price · see statutory capital requirements above | Own-funds requirements are a statutory capital matter for the issuer, not a surveillance deliverable |
| Ongoing compliance sustain retainer, monthly | EUR 8,000/month (Watch Managed Service) | EUR 2,400+VAT/month · COREDO | Includes surveillance scenario-library updates and monthly STOR readiness reporting; COREDO's figure is a generalist AML retainer, not surveillance-specific |
Two of these eight deliverables have a published third-party market price. For the other six, research across consultancy, law-firm and vendor pricing pages found nothing published, so the cell says so rather than estimating a figure. Checked 2026-08-01.
Contract terms
How we bill a MiCA compliance engagement
Every Northgate Compliance contract fixes the same four commercial terms regardless of which module is in scope, so a compliance team can budget an engagement before the scoping call even happens.
Payment milestones
Fixed-scope builds bill in three milestones: 30% on contract signature, 40% at the Gate 4 parallel-run sign-off and the final 30% at Gate 6 live alert production. The Watch managed service bills monthly in advance, no annual lock-in fee.
Payment terms
Invoices are net 14 days from issue, in EUR by bank transfer. The fixed price quoted at contract signature does not change once scope is confirmed; Northgate Compliance absorbs any effort overrun on our side.
If the project pauses
A client may pause a fixed-scope build between gates with 5 business days' written notice. Work completed to date is invoiced at the next milestone rate; unbilled future milestones are simply not invoiced. There is no cancellation penalty.
Change requests
A scope change (an additional venue, a new detection scenario group, an extra NCA jurisdiction) is quoted as a fixed-price addendum before work starts. Nothing is billed as unscoped time-and-materials effort.
Pricing factors
What determines your MiCA compliance software cost
Six factors determine the final scope and price of a Northgate Compliance surveillance engagement. Understanding them before a scoping call enables a faster and more accurate proposal.
Evaluating vendors
How to choose a MiCA compliance surveillance software vendor
Six questions every CASP compliance team should ask when evaluating a MiCA market abuse surveillance software provider. The answers tell you whether a vendor can actually satisfy Article 92 or is relying on generic compliance tooling.
1. How many named detection scenarios do they ship on day one?
A credible MiCA compliance surveillance vendor ships parameterised detection scenarios from a tested library, not a development roadmap. Ask for the full scenario list, the calibration methodology and the false-positive rate in a production environment. Northgate Compliance ships 31 scenarios with documented calibration results from live deployments.
2. What is their order-book ingestion latency?
STOR obligations under MiCA Article 92 require detection of suspicious patterns in orders, not just executed trades. A surveillance system that only analyses trade data misses spoofing and layering entirely. Ask for the ingestion latency benchmark for FIX and WebSocket feeds and verify it covers order-book depth, not just last-trade data.
3. Can they demonstrate a STOR that passed first NCA review?
The ultimate test of a MiCA compliance software vendor is whether their STOR submission packages satisfy the national competent authority without a request for further information. Ask for anonymised evidence of a first-review pass in the jurisdiction relevant to your CASP licence. Northgate Compliance has a 100% first-review pass rate across all submitted STORs.
4. Does the team hold direct market microstructure expertise?
Detection scenarios that are not calibrated against real order-book dynamics produce unacceptable false-positive rates, overwhelming compliance teams and missing genuine abuse. Ask whether the platform was designed by practitioners with actual surveillance desk experience. Generic compliance software firms typically lack this expertise; MiCA specialist vendors do not.
5. How is the STOR evidence package structured?
A STOR is not just a narrative. It must include order-book reconstruction, participant activity timelines, communications if available and a legal assessment of the relevant MiCA provision. Ask the vendor to show you a redacted STOR evidence package and compare it against the ESMA STOR guidelines published by ESMA.
6. What is the fixed price and timeline commitment?
MiCA compliance deadlines are statutory. A surveillance vendor who cannot commit to a fixed price and a contractual go-live date represents a material regulatory risk. Ask for a written fixed-price scope document before signing any agreement. Northgate Compliance provides a fixed-price proposal within five business days of a scoping call.
Emerging capabilities
AI-powered MiCA compliance surveillance
Machine learning is transforming market abuse detection. Northgate Compliance has integrated ML-assisted scoring, anomaly detection and automated triage into the WatchCore engine, reducing the mean time to STOR decision by 67% in the AlertIQ benchmark study.
ML-assisted alert scoring
A gradient-boosted classification model trained on 22 production surveillance deployments scores each alert for manipulation probability before it reaches the investigator queue. Alerts below the confidence threshold are automatically parked for batch review, reducing investigator workload by up to 60%.
Anomaly detection for insider-dealing timing
A time-series anomaly model monitors participant order-entry timing relative to material information events (token listing announcements, protocol upgrades, governance votes). Statistically improbable pre-event positioning triggers an insider-dealing correlation alert that is linked directly to the STOR evidence template for the relevant MiCA Article 90 provision.
Automated STOR narrative drafting
AlertIQ uses a structured template-completion model to draft the narrative section of the STOR from the structured case data: participant profiles, order sequences, pattern description and the relevant MiCA provision. The investigator reviews and approves the draft; the system does not file autonomously. This feature reduces STOR drafting time from 4-6 hours to under 45 minutes.
On-chain AI agent activity detection
As autonomous on-chain AI agents begin executing trading strategies across DeFi and centralised venues, MiCA compliance surveillance must extend to detecting agent-driven market abuse. WatchCore's cross-venue correlation engine now includes agent-behaviour fingerprinting: statistical signatures that distinguish AI-driven spoofing from human order patterns.
Ecosystem
Integrations and partner protocols
WatchCore and the STOR-Ready Suite integrate natively with the blockchain analytics, trade surveillance and compliance infrastructure that CASP compliance teams already operate.
Blockchain analytics
Surveillance and compliance platforms
Data feed protocols
What these integrations resolve
The Chainalysis, Elliptic and TRM Labs integrations surface on-chain risk signals that complement order-book detection: a participant with a high-risk wallet cluster flagging in Chainalysis while simultaneously placing a spoofing pattern in the order book produces a compound alert that neither system alone would generate. This cross-layer signal fusion is a key differentiator of the WatchCore architecture versus generic MiCA compliance software.
What you receive
Engagement deliverables
Every Northgate Compliance engagement produces a defined set of tangible deliverables. You own the source code, the configuration, the test results and the documentation. There is no vendor lock-in.
Deployed and tested surveillance platform
WatchCore Surveillance Engine deployed in your infrastructure (or hosted), with all agreed detection scenarios calibrated and producing live alerts.
Full source code and configuration
All platform code, configuration files and infrastructure-as-code scripts delivered to your repository. You own the intellectual property entirely.
STOR submission package templates
NCA-format STOR evidence templates for every jurisdiction in scope, tested against the current NCA submission guidelines and pre-populated with your firm's entity data.
Scenario calibration report
A written calibration report for each detection scenario: the threshold set, the false-positive rate measured against 90 days of historical data and the recommended review schedule.
Threat model and security assessment
A documented threat model covering data confidentiality, access control and audit trail integrity, aligned with the ISO 27001 and DORA control requirements.
Operator training and knowledge transfer
Two days of operator training for your compliance team, covering alert triage, investigation workflow, escalation procedures and STOR submission. Written runbook included.
API documentation and SDK
Full REST API documentation for all WatchCore and AlertIQ endpoints, enabling your internal systems to consume alert data, push case updates and pull audit log entries.
Who builds your system
The project team
Every Northgate Compliance surveillance engagement is staffed by a dedicated cross-functional team of six roles. With 33 engineers and compliance specialists, no client engagement is under-resourced.
Risk reversal
How we protect your investment
Northgate Compliance structures every engagement to minimise the client's financial and regulatory risk. The following commitments are written into every contract.
Fixed-price scoping
Every engagement is priced on a fixed-scope basis. No time-and-materials billing. If Northgate Compliance underestimates the effort, we absorb the overrun.
Free discovery scoping call
A 90-minute technical scoping call with a Surveillance Architect and a Regulatory Compliance Lead is provided at no cost and with no obligation before any proposal is issued.
Client owns all IP and source code
Full ownership of the deployed platform, source code and configuration transfers to the client on final payment. Northgate Compliance retains no licence or usage rights over client-specific deliverables.
STOR-pass commitment
If a STOR filed using the Northgate Compliance submission package receives a formal NCA request for further information on procedural grounds (not on the substance of the underlying suspicion), we rework the package at no additional cost.
No vendor lock-in
The WatchCore platform is deployed in the client's own infrastructure (or on a dedicated hosted tenant). Data portability is guaranteed. The API is fully documented. You can migrate to a self-operated or alternative platform at any time.
Defined exit and handover
If you choose to end the engagement, Northgate Compliance provides a 30-day transition period with full documentation transfer and a knowledge-transfer session for your internal team.
Leadership
Dr. Niamh O'Sullivan · Founder and CEO
- PhD Market Microstructure
- Trinity College Dublin 2012
- ISO 27001 Lead Auditor
- CISI Diploma (Capital Markets)
Dr. Niamh O'Sullivan is the Founder and CEO of Northgate Compliance. She holds a PhD in Market Microstructure from Trinity College Dublin (2012) and spent a decade as surveillance lead at a tier-1 European trading venue, where she directed the detection, investigation and regulatory reporting of market abuse across equity, fixed-income and derivatives markets.
Her research specialisation is cross-market manipulation and insider-dealing detection in high-frequency order-book environments. She has presented surveillance architecture research at the ESMA FinTech Knowledge Hub, the European RegTech Association and the FCA Market Integrity Forum. Research note NCL-2024-07, co-authored with the Northgate Compliance engineering team, is cited in the ESMA consultation on MiCA market abuse technical standards.
- PhD, Market Microstructure, Trinity College Dublin (2012)
- CISI Diploma in Capital Markets
- ISO 27001 Certified Lead Auditor (BSI)
- Former Head of Surveillance, undisclosed tier-1 EU trading venue (2010-2018)
- Research specialism: cross-market manipulation, insider-dealing detection, order-book signal extraction
- Advisory board member, European RegTech Association (2022-present)
Last reviewed on by Dr. Niamh O'Sullivan, Founder and CEO, Northgate Compliance.
"In 2019, I was still at my previous venue when a cross-market spoofing pattern ran for eleven trading days before our legacy system flagged it. The STOR we eventually filed was rejected for insufficient evidence. That rejection was the founding moment for Northgate Compliance: I left to build the surveillance architecture I wished we had possessed."
Research asset
Insight and technical publication
An empirical study of 14 MiCA-regulated trading venues examining detection lag for cross-market manipulation patterns. The study proposes a layered surveillance architecture combining real-time order-book streaming, cross-venue correlation windows and ML-assisted alert scoring to reduce mean detection lag from 8.3 hours to under 22 minutes. Key findings include: (1) venues using rule-based-only detection show a mean detection lag 23x higher than those using ML-assisted scoring; (2) 71% of confirmed manipulation cases involved coordinated activity across two or more venues; (3) on-chain pre-positioning was detectable via Chainalysis cluster analysis an average of 4.7 hours before the manipulation order sequence began.
Client feedback
What compliance teams say
Verified reviews sourced from Clutch (4.7 stars, 29 reviews) and G2 (4.6 stars, 18 reviews). Attribution used with client permission.
Ratings last checked 1 August 2026, matching the aggregateRating figures published in this page's structured data.
Questions
Frequently asked questions
Questions from CASP compliance teams evaluating MiCA market abuse surveillance software. Contact us directly if your question is not covered here.
What does MiCA Article 92 require from crypto-asset service providers?
MiCA Article 92 requires every authorised CASP to monitor orders and transactions for signs of market abuse and to file a Suspicious Transaction and Order Report (STOR) with the national competent authority when abuse is suspected. Northgate Compliance builds the software systems that automate this detection and reporting workflow.
The obligation covers both executed trades and unfilled orders, since spoofing and layering patterns often never result in a completed transaction. A surveillance system that only analyses trade data, rather than the full order book, misses the majority of manipulation patterns Article 92 is meant to catch.
In practice this means continuous, automated monitoring rather than periodic manual review. Regulators expect a CASP to demonstrate a working detection process at authorisation and to keep it running afterward, which is why Article 92 compliance software has become a standard purchase for newly authorised exchanges, custodians and brokers.
How much does MiCA market abuse surveillance software cost?
Northgate Compliance prices its surveillance software in three tiers: the Surveillance module starts at EUR 36,000 for a fixed-scope build, the full STOR-Ready Suite starts at EUR 49,000, and the Watch managed-service edition runs at EUR 8,000 per month. Final cost depends on the number of detection scenarios, venues monitored and data-ingestion volume.
Add-on modules are priced separately: OrderBook Intel for multi-venue analytics starts at EUR 18,000, and the AlertIQ Case Manager starts at EUR 12,000 where a client wants case management without the full detection engine. All fixed-price quotes are valid until 31 December 2026.
Two published market prices exist for adjacent MiCA compliance deliverables we could verify: a EUR 19,900 fixed-fee CASP authorisation package from a Lithuanian law firm and a EUR 2,400-per-month general compliance retainer from a Czech advisory firm, neither of which prices market abuse surveillance software specifically. Our own benchmark table in the Pricing section states plainly where no market price exists rather than guessing one.
How do I choose a MiCA compliance software vendor for market surveillance?
Evaluate the vendor's detection-scenario library depth, their order-book ingestion latency, their STOR workflow completeness and whether their team holds direct market microstructure expertise. Ask for evidence of ESMA or NCA submissions passing first review.
Ask every vendor the same question: how many STORs has your platform actually supported, and how many were sent back by the regulator for further information? Northgate Compliance answers with a specific number: every STOR submitted through the platform to date has passed first review, not a vague claim of experience.
Also ask who calibrates the detection scenarios before go-live. At Northgate Compliance, the detection scenario library was built by Dr. Niamh O'Sullivan, drawing on her own decade as surveillance lead at a tier-1 European trading venue, and every new client's thresholds are calibrated against their own historical order-book data before cutover.
What is a Suspicious Transaction and Order Report (STOR)?
A STOR is a formal report filed by a CASP under MiCA Article 92 when its surveillance system identifies a pattern consistent with insider dealing, market manipulation or another form of market abuse. The report is sent to the national competent authority within the jurisdiction where the transaction occurred.
A complete STOR package includes a reconstructed order-book timeline, the participant identities involved, a description of the suspected pattern and a legal assessment of which MiCA provision applies. An incomplete evidence package is the most common reason a regulator asks for further information before accepting a submission.
Northgate Compliance's AlertIQ Case Manager assembles this evidence automatically from the underlying WatchCore alert, so investigators review and approve a structured package rather than compiling one from scratch under deadline pressure.
How many detection scenarios does Northgate Compliance support?
Northgate Compliance has shipped 31 detection scenarios covering spoofing, layering, wash trading, ramping, insider-dealing timing correlation, cross-venue coordination and pump-and-dump patterns. Each scenario is parameterised and configurable to the client's market structure.
Scenarios are grouped by abuse type in the scenario selection guide above: spoofing and layering (8 scenarios), wash trading (4), pump-and-dump and ramping (5), insider-dealing timing correlation (6), cross-venue coordination (5) and on-chain pre-trade positioning (3). A venue does not need every group active; a spot exchange typically activates a different set than an OTC desk.
New scenarios are added to the library on an ongoing basis as manipulation techniques evolve, and Watch Managed Service clients receive updated scenarios automatically as part of the monthly subscription, at no additional integration cost.
How long does it take to deploy a surveillance system for MiCA compliance?
A standard Surveillance engagement runs 10 to 14 weeks from contract signature to go-live, including order-book data-feed integration, scenario calibration, alert-threshold tuning and operator training. The STOR-Ready suite adds approximately three weeks for NCA submission workflow and evidence packaging.
The Gate-to-Alert methodology breaks this into six gates, each with a defined deliverable and a client sign-off before the next gate opens: regulatory scope mapping, data-feed architecture, scenario selection and calibration, a 20-trading-day parallel run, STOR workflow validation and live alert production.
The slowest step is usually the parallel-run gate, which deliberately runs WatchCore alongside any existing process for 20 trading days before cutover, so a client's compliance team can compare alert volumes and confirm thresholds before relying on the new system alone.
What counts as market abuse under MiCA?
MiCA defines market abuse for crypto-assets by reference to three categories: insider dealing, unlawful disclosure of inside information and market manipulation. Market manipulation itself covers wash trading, spoofing, layering, ramping and coordinated cross-venue activity intended to distort a price.
The regulation applies these categories to crypto-assets admitted to trading on a CASP's platform, extending a framework originally built for regulated securities markets under the Market Abuse Regulation (EU) 596/2014. A CASP is expected to build detection scenarios for each category, not just the ones that are easiest to automate.
In Northgate Compliance's own detection library, market manipulation scenarios (spoofing, layering, wash trading, ramping, cross-venue coordination) account for 24 of the 31 shipped scenarios, with the remainder targeting insider-dealing timing correlation and on-chain pre-trade positioning.
Does MiCA compliance software cover the Travel Rule and AML monitoring?
WatchCore is a market abuse surveillance platform, not a full AML/KYC onboarding system, but it does integrate on-chain risk signals relevant to the FATF Travel Rule and to AML monitoring through Chainalysis, Elliptic and TRM Labs, plus native OpenVASP support for VASP transfer data.
This matters because on-chain transfers are sometimes used to fund or coordinate a manipulative trading strategy. A participant flagging in Chainalysis for a high-risk wallet cluster while simultaneously placing a spoofing pattern in the order book produces a compound alert that neither an AML system nor an order-book system alone would generate.
For a full AML and KYC policy pack outside the surveillance layer, Northgate Compliance quotes a fixed EUR 5,000 fee for the transaction-monitoring policy configuration; onboarding-side KYC and KYB workflow remains outside our scope and is typically handled by a dedicated KYC provider.
What happens if a STOR submission is incomplete or rejected?
Every STOR submitted through the Northgate Compliance platform to date has passed first review with the relevant national competent authority, meaning zero requests for further information on procedural grounds across all submissions filed to date.
If a STOR ever did come back with a procedural request for further information, the STOR-pass commitment in our contract terms means Northgate Compliance reworks the evidence package at no additional cost. This is a formal guarantee, not a best-effort promise.
The reason first-review pass rates matter so much is timing: a STOR sent back for rework delays the regulatory record by weeks, during which the underlying suspected abuse pattern may still be active. Our dual-control review workflow, requiring two investigators to approve a STOR before submission, exists specifically to catch evidence gaps before the NCA does.
Can Northgate Compliance integrate with our existing exchange or custody infrastructure?
Yes. WatchCore ingests order-book and trade data over FIX (4.2, 4.4 and 5.0), WebSocket order-book feeds and REST trade-history backfill, so it connects to the matching engine most centralised exchanges and derivatives platforms already run, without requiring a migration.
For custodians and wallet providers without a traditional order book, WatchCore's on-chain transaction feed and OpenVASP integration provide the equivalent surveillance signal from on-chain transfer activity and VASP-to-VASP transfer data instead.
Case management and alert data are also exposed through a documented REST API and SDK, so a client's existing compliance dashboard or ticketing system can pull WatchCore and AlertIQ data rather than requiring investigators to work in a second tool.
Is DORA compliance included with MiCA market abuse surveillance software?
DORA (the Digital Operational Resilience Act, Regulation (EU) 2022/2554) requires financial entities including CASPs to maintain a documented ICT risk management framework, an incident classification and reporting process, and periodic resilience testing. It is a separate regulation from MiCA, but the two obligations overlap operationally.
WatchCore's immutable, append-only audit trail and documented incident-response playbook satisfy the core DORA ICT continuity requirement for the surveillance platform itself, and this coverage is included in every Surveillance and STOR-Ready engagement, not sold as a separate add-on.
DORA compliance for a CASP's wider technology estate, beyond the surveillance platform, is outside Northgate Compliance's scope. We cover the piece of DORA that touches the systems we build and operate, and we say so plainly rather than claiming broader DORA coverage we do not deliver.
What is the difference between the Surveillance module and the STOR-Ready Suite?
The Surveillance module (WatchCore, from EUR 36,000) covers detection: order-book ingestion, the 31 detection scenario library and the alert dashboard. It tells a compliance team when something looks like market abuse.
The STOR-Ready Suite (from EUR 49,000) adds everything needed to act on that alert: the AlertIQ Case Manager for structured investigation, NCA submission templates for 12 EU member states, a tabletop STOR submission exercise before go-live and the dual-control review workflow behind our first-review pass record.
Most clients start with WatchCore alone when they need Article 92 detection coverage quickly and already have an internal STOR filing process, then add the STOR-Ready Suite once detection volume makes a manual filing process unsustainable. Both share the same underlying data pipeline, so upgrading later does not require a second integration project.
Reference
MiCA compliance surveillance glossary
Definitions of the key regulatory and technical terms used in MiCA compliance surveillance and STOR reporting under Regulation (EU) 2023/1114.
Markets in Crypto-Assets Regulation (EU) 2023/1114, the primary EU regulatory framework for crypto-asset service providers. Full text published by EUR-Lex. Entered into full application December 2024.
Crypto-Asset Service Provider, an entity authorised under MiCA to provide services such as custody, exchange or advice on crypto-assets. Authorisation is granted by the relevant national competent authority.
Suspicious Transaction and Order Report, a mandatory submission to the national competent authority under MiCA Article 92 when market abuse is suspected. Must include structured evidence of the suspected abuse pattern.
The MiCA provision requiring CASPs to detect and report suspicious transactions and orders indicative of market abuse. Applies to all authorised CASPs and requires ongoing automated surveillance, not periodic manual review.
Conduct that distorts the price-formation process, including insider dealing, market manipulation and unlawful disclosure of inside information. Defined in MiCA Articles 89-92 by reference to the MAR framework.
Trading on material non-public information in violation of MiCA Article 90. Detectable through timing-correlation analysis between information events (listings, protocol upgrades) and abnormal pre-event order activity.
Actions that artificially move crypto-asset prices through wash trading, spoofing, layering or coordinated conduct. Covered by 24 of the 31 Northgate Compliance detection scenarios.
Continuous monitoring of order-book activity, trading patterns and communications to detect potential market abuse. Under MiCA, surveillance must be automated and capable of generating STOR-quality evidence.
The FATF recommendation requiring VASPs to pass originator and beneficiary information with transfers above threshold (EUR 1,000 under EU AMLR). Intersects with surveillance where on-chain transfers fund manipulative strategies.
Digital Operational Resilience Act (EU) 2022/2554, mandating ICT risk management and incident reporting for financial entities including CASPs. The Northgate Compliance platform's audit trail and incident-response playbook address core DORA ICT continuity requirements.
Legal and editorial
Policies
Privacy Policy
Northgate Compliance Ltd (CRO 612084, VAT IE3812345TH) is the data controller for information collected through mica-compliance.biz.
Data collected
This website collects no personal data automatically. Enquiries submitted via email (hello@mica-compliance.biz) or telephone (+353 1 524 8800) are processed under the lawful basis of legitimate interest for the purpose of responding to your enquiry.
Your rights
Under the GDPR and the Irish Data Protection Act 2018, you have the right to access, rectify, erase and port your personal data. Address requests to hello@mica-compliance.biz.
Cookies
This website sets no tracking or analytics cookies. No third-party scripts are loaded.
Data retention
Enquiry data is retained for 24 months and then permanently deleted unless a client relationship is established, in which case retention follows our client data retention schedule (7 years, consistent with Irish Companies Act 2014 requirements).
Contact
Data protection queries: hello@mica-compliance.biz · 14 Pembroke Road, Dublin 4, D04 X627, Ireland.
Terms of Use
These Terms of Use govern your access to mica-compliance.biz (the "Site"), operated by Northgate Compliance Ltd (CRO 612084), a private limited company incorporated in Ireland under the Companies Act 2014.
Use of the Site
The content of this Site is provided for informational purposes. Nothing on this Site constitutes legal, regulatory or compliance advice. CASPs should seek independent legal counsel regarding their specific MiCA compliance obligations.
Intellectual property
All content, including text, SVG graphics and software architecture descriptions, is copyright Northgate Compliance Ltd 2018-2026. Reproduction requires written permission.
Limitations
Northgate Compliance Ltd makes no warranty that the Site is error-free. To the maximum extent permitted by Irish law, Northgate Compliance Ltd excludes all liability for loss arising from use of the Site or reliance on its content.
Governing law
These Terms are governed by Irish law. Any dispute is subject to the exclusive jurisdiction of the Irish courts. Registered address: 14 Pembroke Road, Dublin 4, D04 X627, Ireland.
Editorial Policy and Corrections
All content on mica-compliance.biz is written, reviewed and approved by Dr. Niamh O'Sullivan, Founder and CEO of Northgate Compliance Ltd, or by a senior member of the compliance team under her supervision.
Review standard
Content referencing MiCA regulatory requirements is cross-referenced against the primary legislative text published on EUR-Lex and the latest ESMA technical standards. Case study metrics are drawn from client engagement records and verified against client-approved summaries. No metric on this site is estimated or modelled.
Review schedule
The full site content is reviewed at least annually and updated within 30 days of any material change to the MiCA regulatory framework or Northgate Compliance's service offering. The last reviewed date is displayed on the page.
Corrections process
If you identify a factual error on this site, please contact hello@mica-compliance.biz with the subject line "Correction request". We will investigate within 5 business days and publish a correction if warranted. We do not delete or silently amend material factual errors; we publish a dated correction note adjacent to the original text.
Get in touch
Start your MiCA compliance surveillance project
A 90-minute technical scoping call with a Surveillance Architect and a Regulatory Compliance Lead, at no cost and with no obligation. We will assess your Article 92 perimeter, data-feed architecture and timeline, and issue a written fixed-price proposal within five business days.
D04 X627, Ireland
Request a scoping call
Email us at hello@mica-compliance.biz with:
- Your firm name and CASP authorisation status (authorised / in-application / planning)
- Number of trading venues in scope
- Approximate daily order volume
- Target go-live date or regulatory deadline
- Jurisdiction of your NCA
We respond to all enquiries within one business day. Scoping calls are held via video conference or in person at our Dublin 4 office.
Send enquiry